Category: Development
-
MCP vs API: What’s Actually Different, and Why You’ll End Up With Both
MCP doesn’t replace your APIs — it sits on top of them and solves a different problem: letting an AI model discover and use your systems without custom integration code. The real differences, the false dichotomy, and a decision rule for when each applies.
-
Securing MCP in Production: OAuth, Agent Identity, and What a 2026 Security Review Actually Covers
MCP auth has hardened fast — resource indicators, issuer validation, CIMD instead of dynamic registration. But the gaps that hurt companies in production are mostly not in the protocol. What a real MCP security review covers in 2026, layer by layer.
-
How to Build an MCP Server in 2026: From First Tool to Production
Most MCP server tutorials stop at “hello world” — and most were written before the protocol went stateless. The build sequence we use for client work: scoping the tools, choosing the SDK, auth, testing against a real client, and shipping something production actually accepts.
-
2,000 MCP Servers and Counting: How to Choose, Vet, and Connect Them Without Getting Burned
The MCP Registry now lists nearly 2,000 servers, the protocol lives under the Linux Foundation, and MCP Apps put interactive interfaces inside the chat. A practical guide to picking connectors you can trust — and knowing when to build your own instead.
-
MCP Goes Stateless: What the July 2026 Spec Overhaul Means for Your AI Integrations
The 2026-07-28 MCP specification is the biggest rewrite since the protocol launched — stateless by default, cheaper to scale, and with a 12-month clock on several things your integration may depend on. What changed, and what to actually do about it.
-
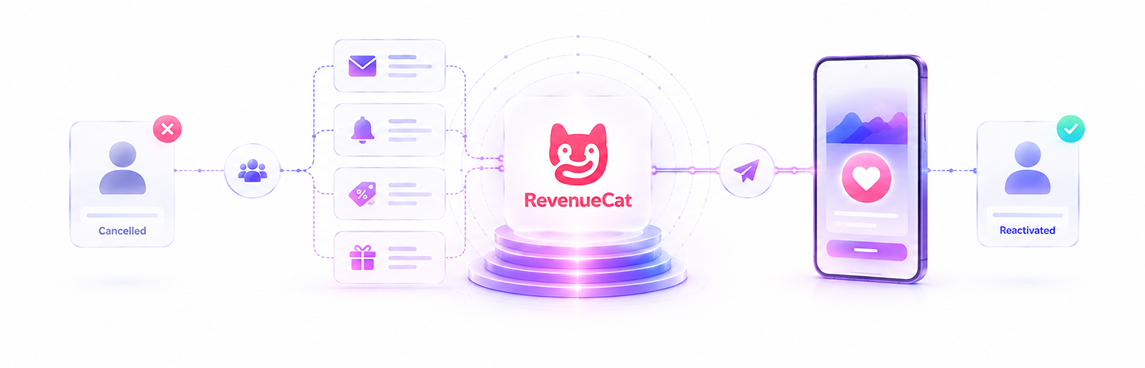
Win-Back Campaigns for Cancelled Subscribers: What to Automate with RevenueCat
Most subscription teams spend heavily on acquisition and almost nothing on winning back the subscribers who already tried the product and left. The signals worth automating on, and the store rules that constrain what a win-back offer can actually do.
-
Family and Group Plans in RevenueCat: Sharing One Subscription Across Multiple Users
A family or team subscription is a different entitlement problem than a single-user one — one purchaser, multiple beneficiaries, and access that has to survive someone leaving the plan. How we model shared access on top of RevenueCat’s single-user entitlement primitive.
-
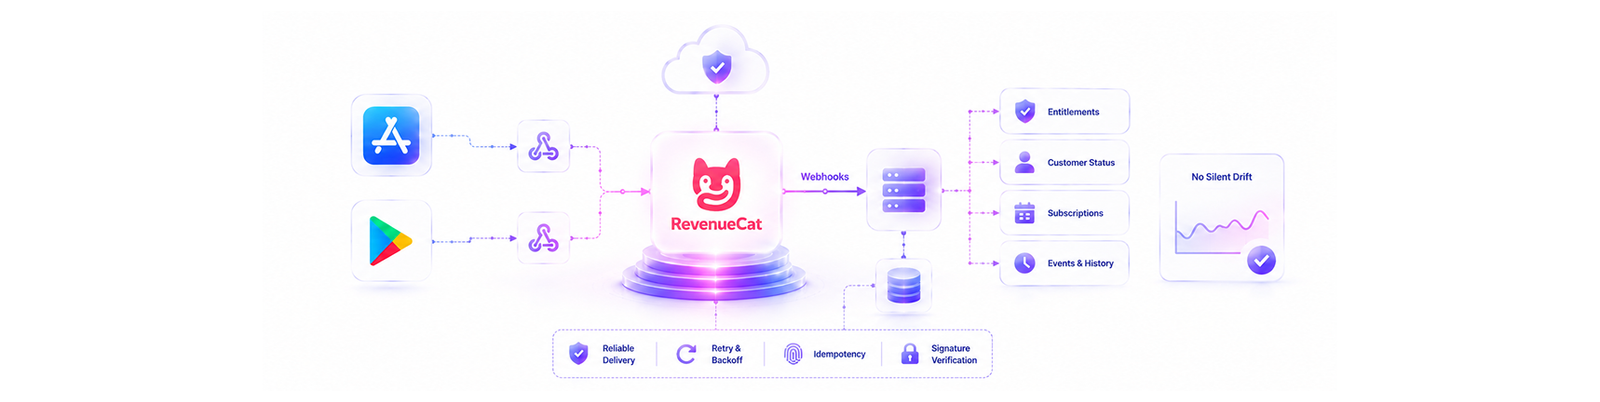
Webhook Architecture for RevenueCat: Building a Backend Sync That Doesn’t Silently Drift
Most RevenueCat webhook integrations work fine until an event arrives twice, arrives out of order, or your endpoint is down for ten minutes. The queue-based pattern that survives all three, and the failure modes it’s specifically designed around.
-
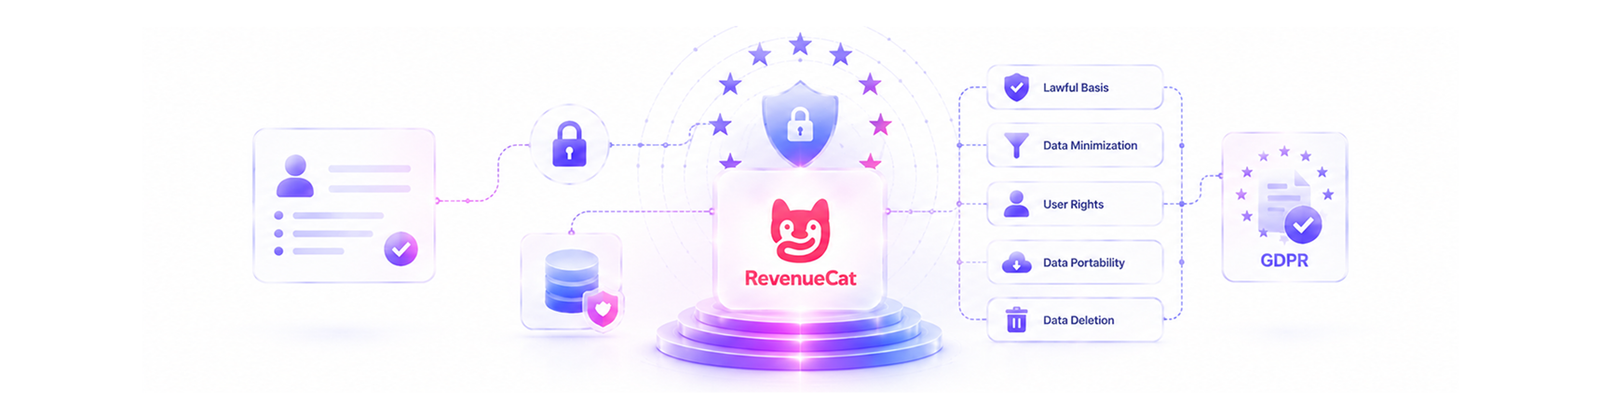
GDPR and Subscriber Data in RevenueCat: What a Compliance Review Actually Covers
Any subscription app with European users is handling personal data through a billing platform, whether or not the product itself is sensitive. What a GDPR review of a RevenueCat integration actually looks at — distinct from the health-specific compliance questions we cover elsewhere.
-
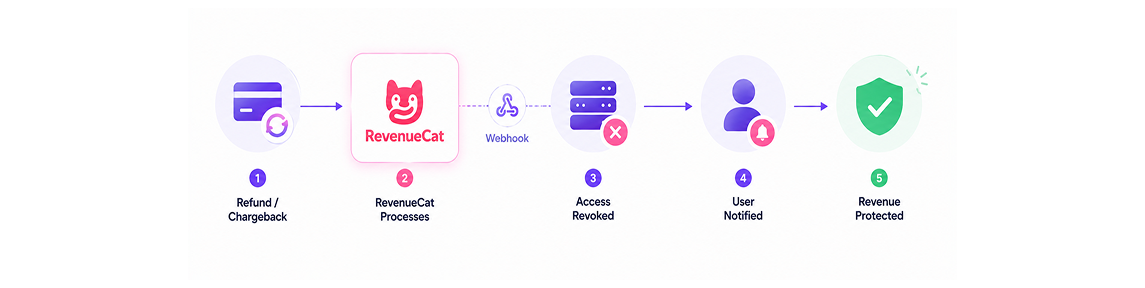
Refunds, Chargebacks, and Entitlement Revocation: What Happens When the Money Comes Back
A refund and a chargeback both end with revoked access, but they arrive differently, on different timelines, and with different fraud implications. What to actually build so a subscriber’s access changes the moment the store says it should.